GSE·SW · Activity Control
Your data is locked before the system even boots
Activity Control sits in the UEFI BIOS, encrypts entire drives and lets no one near the machine without pre-boot authentication. Developed by GSE and certified by the KNB of Kazakhstan at trust level 5.
- Algorithms
- AES-256, Serpent, Twofish
- Platforms
- Windows, Linux
- Firmware
- UEFI and legacy BIOS
- Authentication
- Password, key file, token
State certification
5trust level
The highest KNB trust level in Kazakhstan
Activity Control is certified by the National Security Committee of the Republic of Kazakhstan at trust level 5, the highest there is. These are the strictest requirements for protecting information of national importance.
Cryptographic protection
A certified cryptographic information protection tool.
Information of national importance
The trust level required for systems that hold the most sensitive data.
Kazakhstan law
Meets Kazakhstan's information security requirements.
Certificate issued byNational Security Committee of the Republic of Kazakhstan
Capabilities
Six lines of defence between your data and outsiders
Protection starts in the firmware and closes every route to your data: boot, drives, BIOS settings and external media.
- 01
UEFI integration
Installs directly into the UEFI BIOS and works at the lowest level, before the operating system loads.
- Pre-boot authentication
- MBR and GPT partition protection
- Secure Boot compatible
- 02
Full-disk encryption
Encrypts whole drives with proven algorithms and hardware acceleration.
- AES-256-XTS, Serpent, Twofish
- Cascade encryption
- AES-NI acceleration
- 03
Multi-factor authentication
Sign-in methods for every way of working and every level of secrecy.
- Password and PIN
- Key files
- Hardware tokens and smart cards
- 04
Boot protection
Stops foreign operating systems from starting and the boot loader from being replaced.
- Boot loader integrity checks
- OS allowlist
- Bootkit protection
- 05
BIOS lockdown
Shields BIOS and UEFI settings from unauthorised changes.
- BIOS password
- Locked boot order
- Boot device control
- 06
Many drives at once
Encrypts and manages several drives simultaneously under one control.
- HDD, SSD, NVMe and USB
- Hardware RAID arrays
- External drives
Cryptography
Algorithms trusted worldwide
Activity Control is built on proven cryptographic algorithms recognised by international security standards.
- AES-256
- A symmetric cipher with a 256-bit key, the main algorithm for drive protection.
- Cascade encryption
- Several algorithms in sequence for data that needs a safety margin.
- Hardware acceleration
- AES-NI, AVX2 and SHA Extensions: encryption on the processor's own instructions.
- Key types
- Passwords, key files, tokens and TPM.
- Hidden volumes
- Encrypted partitions that stay invisible to the system.
- Key derivation
- PBKDF2-HMAC and Argon2id turn a password into a strong key.
Specifications
Everything your security team will check
Technical specifications to assess compatibility with your infrastructure.
Encryption
| Encryption algorithms | AES-256-XTS, Serpent, Twofish, Camellia |
|---|---|
| Cascade algorithms | AES-Serpent, AES-Twofish-Serpent, Serpent-AES |
| Hash algorithms | SHA-512, SHA-256, Whirlpool, Streebog |
| Key derivation | PBKDF2-HMAC, Argon2id |
| Key length | 256-bit, 512-bit in cascade |
Compatibility
| Operating systems | Windows 10 and 11, Windows Server 2016 and later, Linux with kernel 4.x and later |
|---|---|
| Firmware | UEFI 2.0 and later, legacy BIOS, Secure Boot compatible |
| File systems | NTFS, FAT32, exFAT, ext4, XFS, Btrfs |
| Drive types | HDD, SSD, NVMe, USB, Hardware RAID |
Hardware requirements
| Hardware acceleration | AES-NI, CLMUL, AVX2, SHA Extensions |
|---|---|
| TPM support | TPM 1.2 and 2.0, optional |
| Memory | 512 MB to boot, 2 GB recommended |
| Boot loader size | up to 32 MB |
Management
| Central management | Enterprise management console |
|---|---|
| Key escrow | Secure master-key storage |
| Remote unlock | Network pre-boot authentication |
| Event audit | Log of every operation |
Deployment
Deployed the way your IT team works
From one executive's laptop to a fleet of thousands of workstations.
Standalone
Protection for individual devices, with no management server.
- No server required
- Local key management
- Suited to smaller fleets
- Minimal infrastructure requirements
Enterprise
Central roll-out and management across a large organisation.
- Single management console
- Group encryption policies
- Active Directory integration
- Central key escrow
Managed service
GSE specialists run the security of your devices for you.
- Turnkey installation and set-up
- Monitoring and support
- Incident handling
- Regular security updates
GSE hardware
Order GSE hardware with Activity Control on board
Add Activity Control to your L200, M200 or S200 order: machines arrive protected, with encryption already configured.
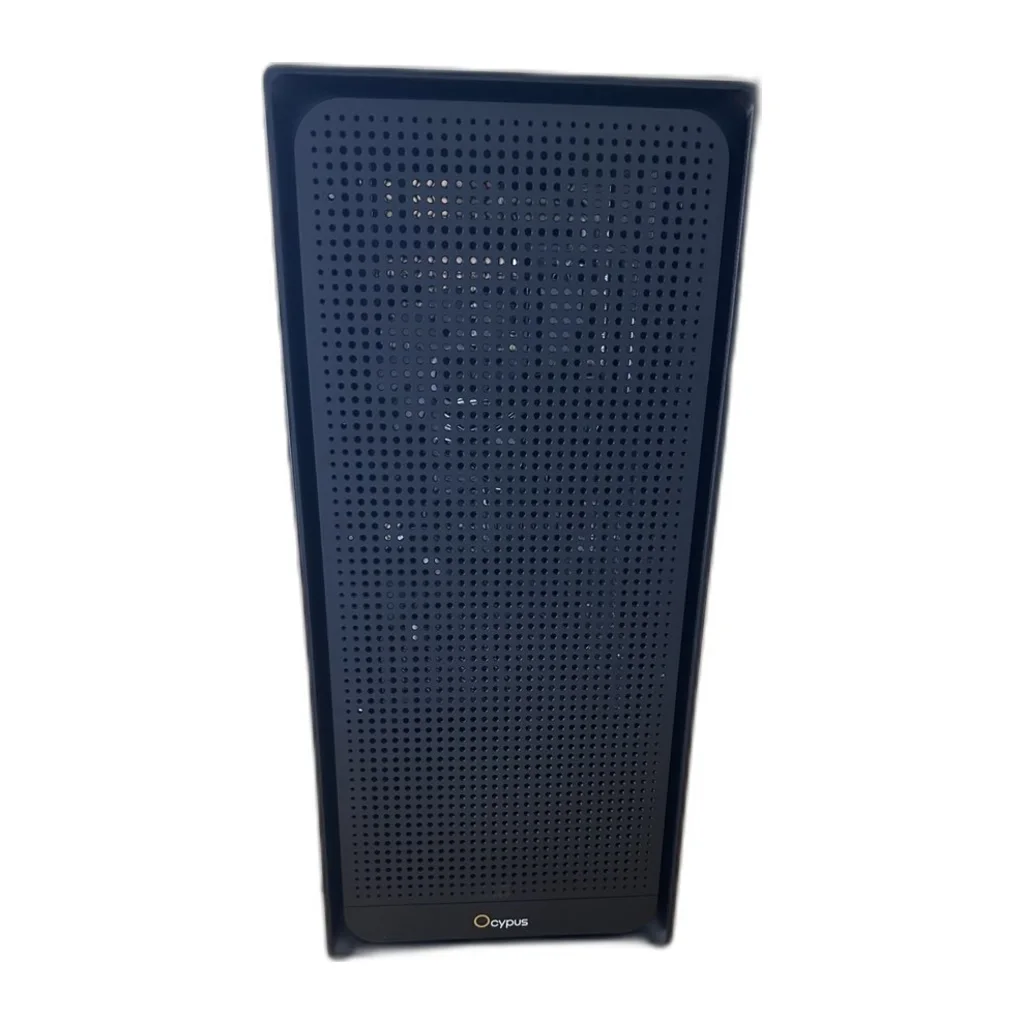
GSE L200 desktops
Workstations from the front office to engineering, on 14th-gen Intel Core and AMD Ryzen.
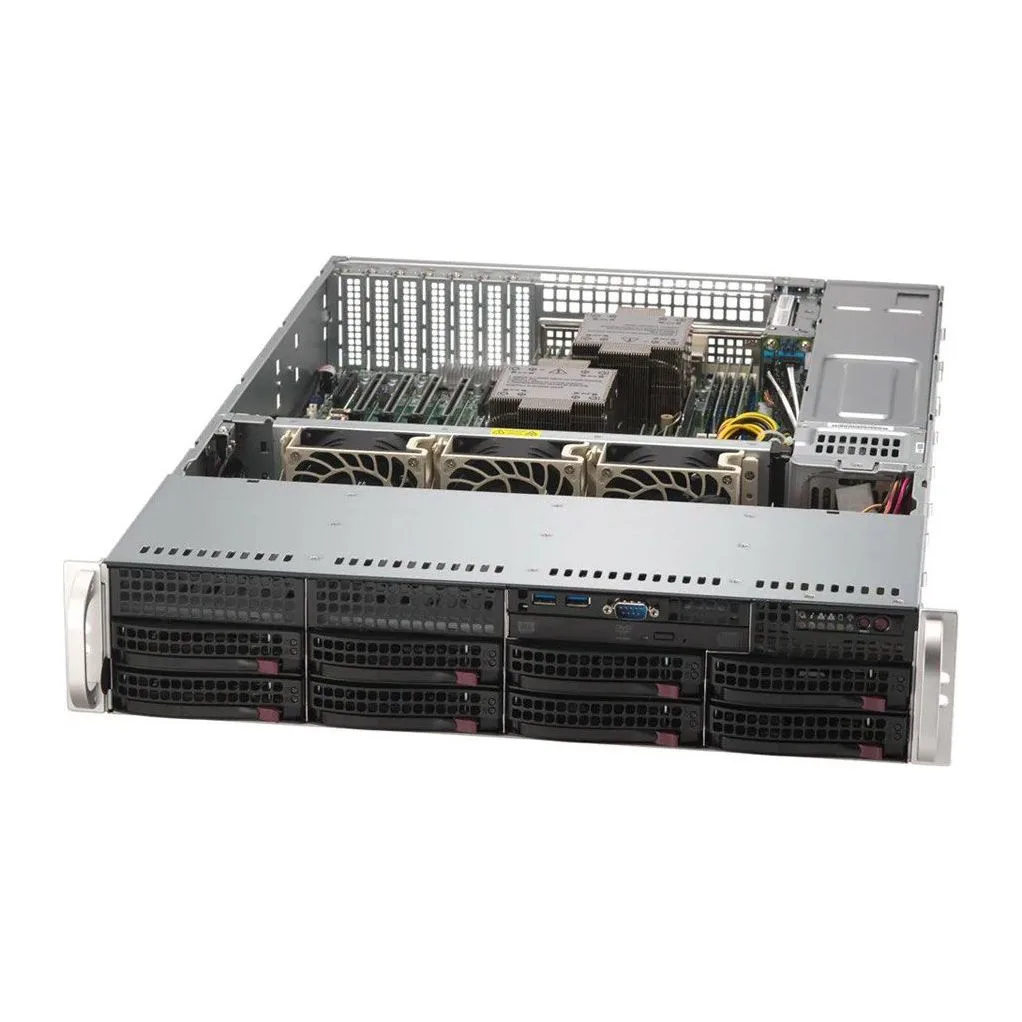
GSE S200 servers
Rack servers on Intel Xeon and AMD EPYC, from a file server to an AI cluster.
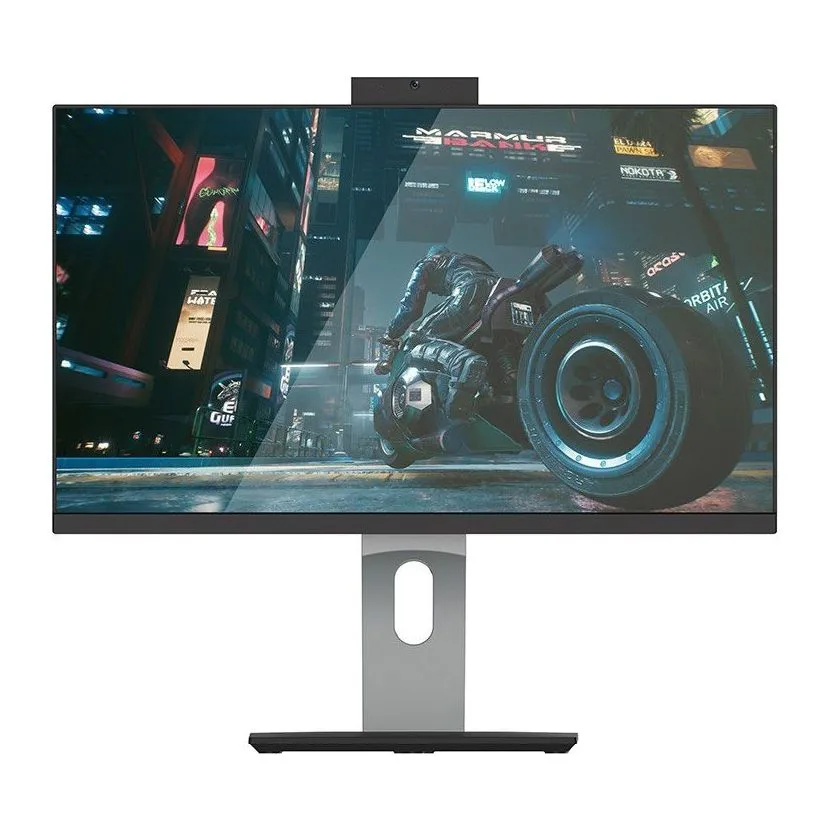
GSE M200 all-in-ones
Screen, computer and camera in one housing, from 21.5 to 34 inches.
Runs on laptops, desktop PCs, servers and storage systems.
Who it's for
For everyone responsible for other people's data
Public sector
Official information and citizens' personal data.
Enterprises
Trade secrets and employee data.
Finance
Regulatory requirements and transaction security.
Healthcare
Medical records and patients' personal information.

Request
Send the specification. We’ll do the rest
One item or a turnkey facility, in any area. One manager runs your delivery from the first call to the commissioning certificate.
Free quoteDocuments for public procurement and tendersOne contract, one warranty